Coinbase Post-Quantum Bitcoin Upgrade Proposal
Written by: David Christopher, Bankless
Compiled by: Saoirse, Foresight News
On October 21, Brian Armstrong shared Coinbase's latest ideas for defending against quantum computer attacks and enhancing Bitcoin security.
The related preparations began in January this year: Coinbase established an independent quantum advisory board, with members including Scott Aaronson, Dan Boneh, Justin Drake, and other cryptography researchers. In July of the same year, Coinbase, in collaboration with BlackRock, Fidelity, Strategy, and other institutions, jointly established the Bitcoin Security Alliance, committing to invest $15 million over the next three years for research in Bitcoin security. Today, Coinbase has fully elaborated on its comprehensive vision for building quantum-resistant Bitcoin, covering new types of addresses, signature schemes, and asset migration plans.
### Designing Iteratively Upgradable Underlying Solutions
Coinbase's core idea: decouple the address container that stores Bitcoin from the signature mechanism that unlocks assets. The address container is used to hold Bitcoin, while the signature mechanism is the way to unlock the assets.
Currently, no one can predict which quantum-resistant signature scheme will provide the highest security and practicality in the long term. Therefore, Coinbase hopes to design a type of address that can be compatible with multiple signature algorithms; when changing cryptographic schemes in the future, there will be no need to redevelop the entire address system.
Coinbase proposed two alternative technical routes: BIP-360 (P2MR), which will introduce a new type of Bitcoin address to reduce the exposure risk of quantum attacks; the other scheme is P2TRv2, which supports quantum-resistant signatures.
Both schemes meet Coinbase's pursuit of flexibility, but neither can be considered a complete solution when used alone. Especially BIP-360, which still requires additional upgrades to support quantum-resistant signatures.
Coinbase also proposed a hybrid address concept: users can either continue using existing signatures or use quantum-resistant signatures to spend the same funds. However, this scheme has shortcomings: as long as the old signature method is still usable, those funds remain vulnerable to quantum attacks. Hybrid addresses can only serve as a transitional measure, not a long-term solution.
Selecting Compatible Signature Algorithms
After establishing that the address design must have flexibility as a core principle, the next key question is: which quantum-resistant signature algorithm should Bitcoin adopt?
Coinbase listed four candidate schemes:
· ML-DSA: Based on lattice cryptography, already standardized, with balanced overall performance; the downside is that the signature data size is relatively large.
· SLH-DSA: Also standardized, built on mature hash functions; the signature size is larger than that of ML-DSA.
· FN-DSA (Falcon): Smaller signature size, but high difficulty in achieving secure implementation, and has not yet been standardized.
· SHRINCS: An experimental scheme designed specifically for Bitcoin, with a smaller signature size, but very strict requirements for key management.
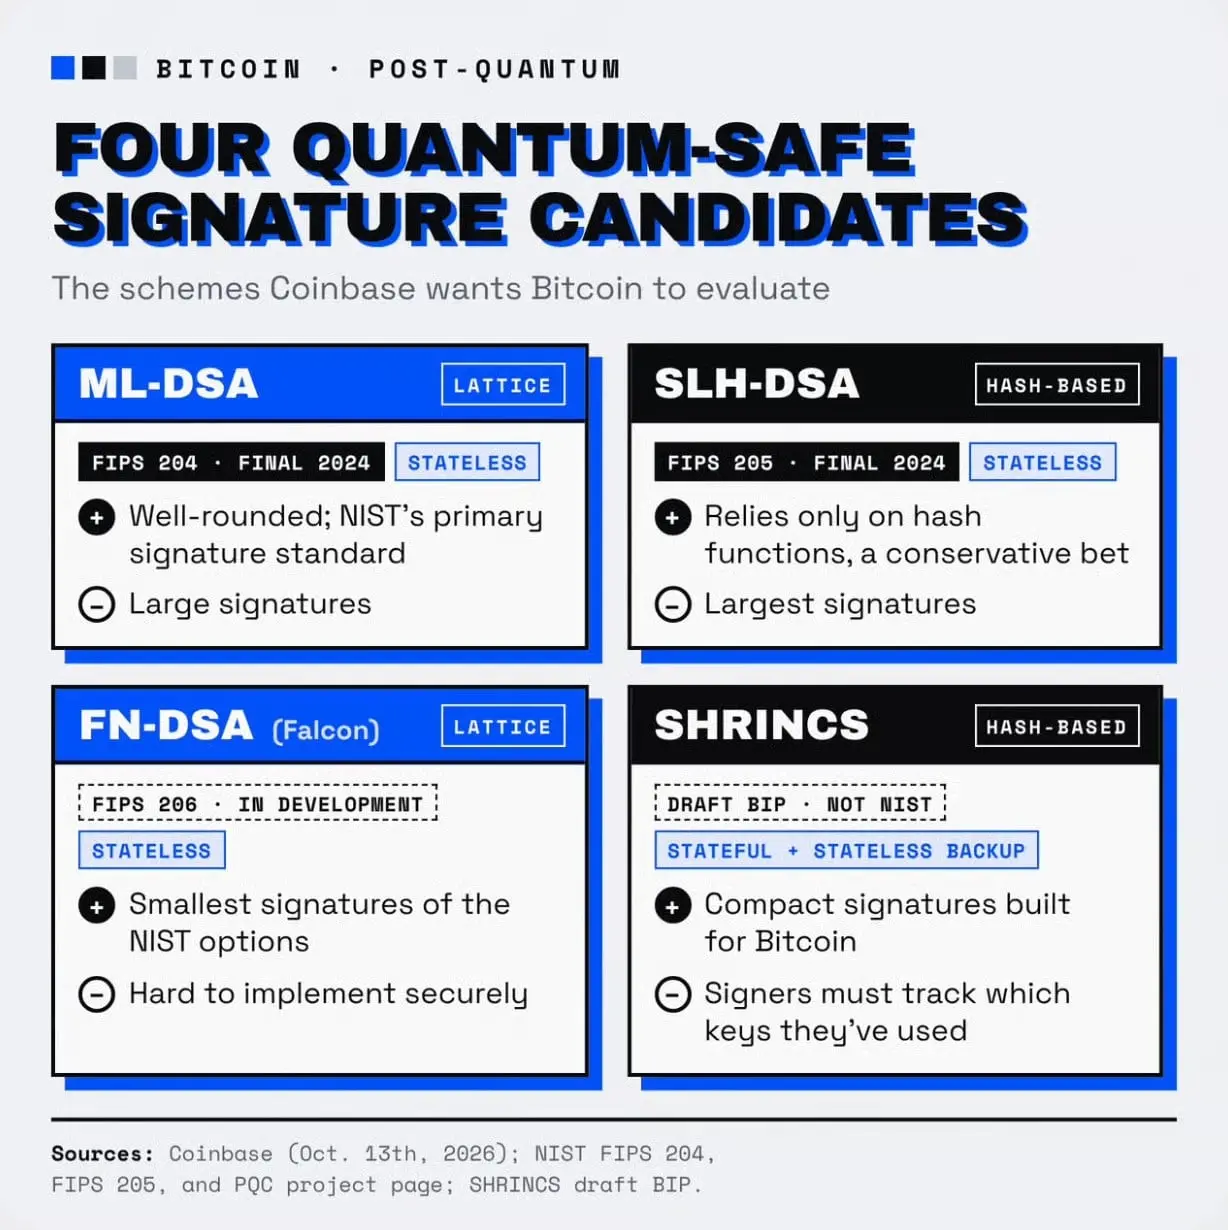
Coinbase proposed four quantum-resistant signature candidate algorithms for Bitcoin evaluation: lattice-based ML-DSA, FN-DSA (Falcon), hash-based SLH-DSA, and SHRINCS, each with its advantages and disadvantages in terms of signature size, implementation difficulty, and whether there is a NIST standard.
The biggest contradiction in the scheme selection comes from the signature size. Quantum-resistant signatures have a data volume much larger than the signatures currently used by Bitcoin, which will occupy more block space, potentially reducing network transaction throughput and increasing transaction fees.
Therefore, Coinbase suggests evaluating different schemes from multiple dimensions, including security, usage costs, processing speed, hardware wallet compatibility, and the migration cycle of high-risk Bitcoin assets.
Another factor to consider is the key management model.
Stateful Signatures: Require users to keep track of the usage records of each signature key. If a key is accidentally reused after restoring from an old wallet backup, an attacker could forge signatures and steal assets. Given the risks, why consider it? The advantage lies in efficiency. The size of stateful signatures can be made smaller, potentially maintaining lower fees, but the risks increase accordingly. Thus, Coinbase recommends that Bitcoin also support stateless signatures, which do not require tracking key usage status.
In addition, Coinbase hopes that the signature scheme can adapt to institutional custody service providers. Many institutional custody businesses use multi-signature architectures, where private keys are split and stored across multiple servers. Some lattice cryptography schemes are more suitable for such architectures, and compatibility is also an important evaluation criterion.
Of course, Coinbase has its own commercial considerations. As one of the largest custodians of Bitcoin, it hopes that the upgrade scheme can be compatible with its own security infrastructure. However, institutions hold a large amount of Bitcoin, and their needs cannot be ignored in the overall Bitcoin ecosystem.
### Phased Approach to Asset Migration
Beyond selecting the signature scheme, Coinbase's goal is to create a clear roadmap to guide the gradual migration of Bitcoin assets to quantum-resistant addresses.
The plan outlines five potential implementation phases:
· Early Trial Phase: Allows users to voluntarily transfer assets to quantum-resistant addresses.
· Hybrid Address Phase: Enables hybrid addresses, compatible with both traditional signatures and quantum-resistant signatures, achieving a smooth and gradual transition.
· Secure Migration Phase: Explores technical means to hide public keys during transfers, reducing the exposure to quantum attacks.
· New Rules Implementation Phase: Gradually restricts transfers to old addresses with security vulnerabilities, ultimately prohibiting asset spending from old addresses.
· Final Wrap-Up Phase: Establishes rules for the disposal of remaining assets in old addresses, with optional methods including setting a migration deadline, asset freezing, limiting transaction amounts, or building an asset recovery mechanism.
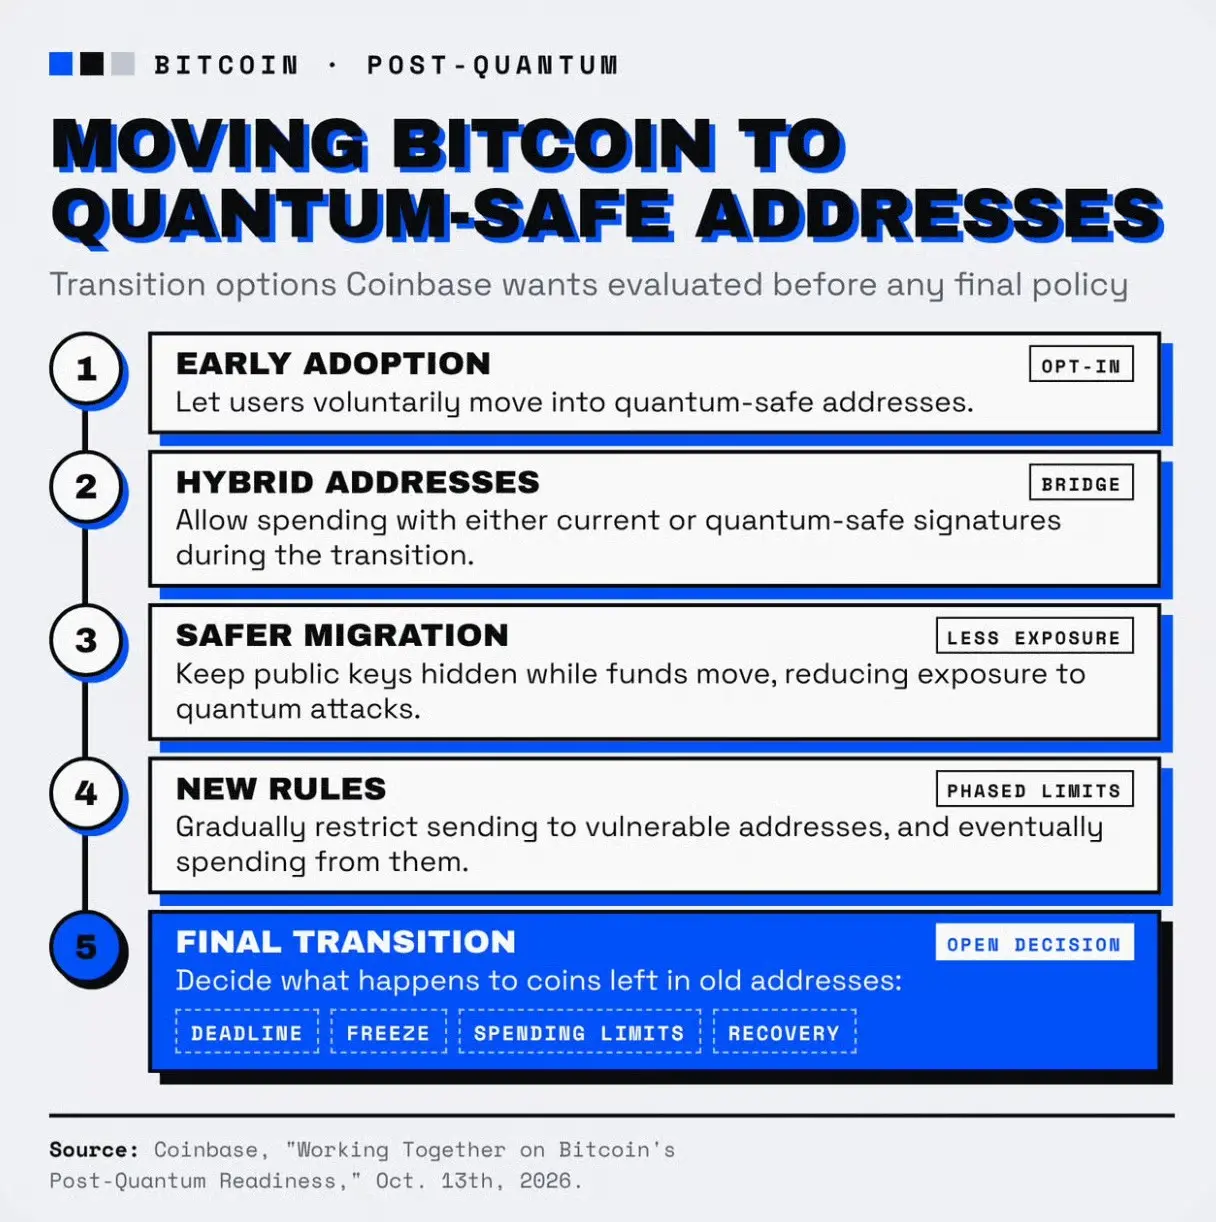
Coinbase proposed five phased alternative plans for migrating Bitcoin to quantum-resistant addresses: from voluntary upgrades by users, hybrid address transitions, hiding public keys to reduce risks, to gradually restricting old addresses, and finally deciding on the disposal methods for remaining assets in old addresses.
Coinbase has not finalized any ultimate plan. The primary task at this stage is to assess the feasibility of various schemes, including the compatibility performance of non-upgraded wallets and nodes, and then determine the final plan based on this.
### Handling Dormant and Lost Bitcoins Separately
Next is the most controversial topic: how to handle Bitcoins that have been dormant for a long time?
Millions of Bitcoins are stored in old addresses where the public keys have already been leaked, including block rewards mined by Satoshi Nakamoto. Some belong to long-term holders, while others may have been permanently lost.
These assets are prime targets for quantum attacks. If someone secretly develops a high-performance quantum computer, they could steal these Bitcoins before the entire industry becomes aware of the risk.
Coinbase neither advocates for direct freezing or forced recovery nor suggests leaving them unattended. Instead, it proposes to separate the discussion of dormant coins from the signature upgrade, avoiding the divergence over dormant Bitcoins from dragging down the quantum security upgrade process for all users.
If an asset recovery mechanism is to be established, Coinbase proposes two hard prerequisites:
· The mechanism itself must possess quantum-resistant characteristics: attackers should not be able to use this recovery mechanism to steal assets solely based on leaked public keys.
· It must cover various extreme scenarios: there should be contingency plans for situations such as holders losing recovery credentials, system overload, or users missing deadlines.
In summary, Coinbase views this proposal as a reference material for public discussion, rather than a final blueprint. No single company or developer can unilaterally decide the direction of Bitcoin's development; achieving consensus across the entire ecosystem is even more challenging than the development of cryptographic technology itself.